
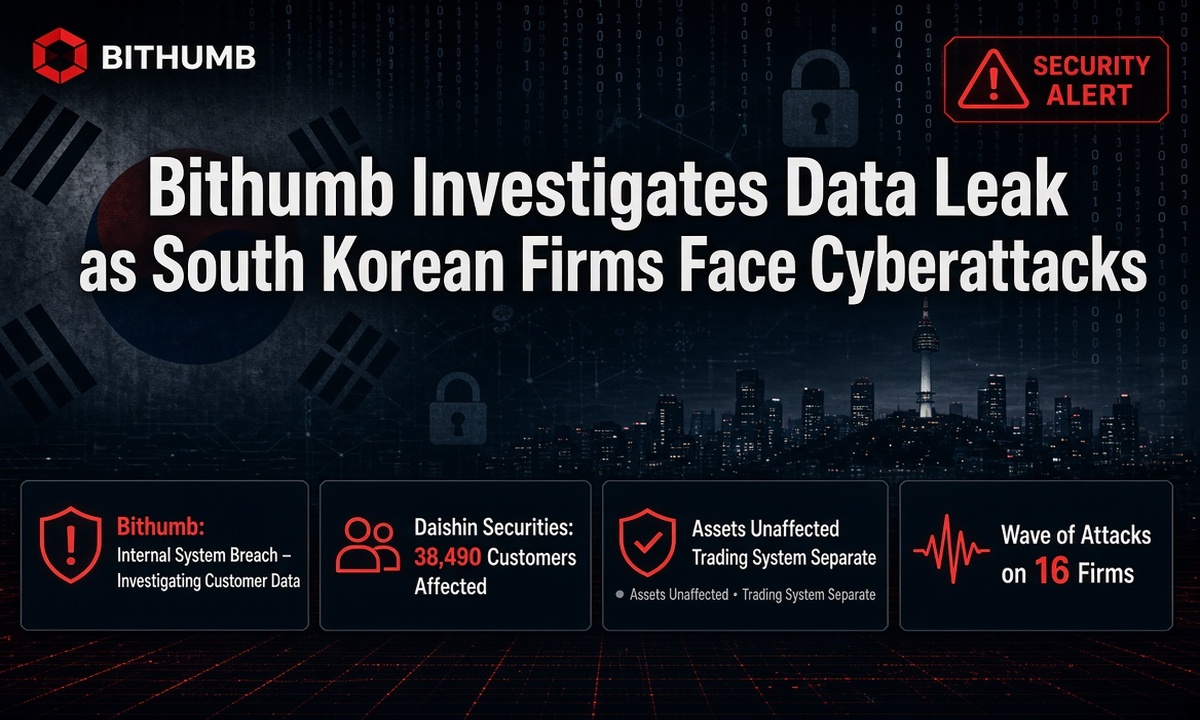
Bithumb, South Korea’s second-largest cryptocurrency exchange by trading volume, is investigating a data breach involving its internal employee system.
The exchange discovered the intrusion on Tuesday, October 27, 2026 and is checking whether hackers accessed customer information.
Bithumb said an unauthorised person accessed its internal mobile groupware system and took personal information. Employees use the system to communicate and share work-related information.
The exchange reported the incident to the Korea Internet & Security Agency and the Personal Information Protection Commission. It has not confirmed how many people the breach affected or whether customer records were exposed.
Bithumb said the affected system operates separately from its trading platform. It reported no stolen crypto assets as of Wednesday afternoon in Asia. However, the exchange has not confirmed whether the breach disrupted deposits or withdrawals.
Bithumb Checks Whether Customer Data Was Exposed
Bithumb is investigating how the attacker accessed its internal system and what information they obtained. The exchange is also checking whether the exposed data included customer details.
The incident comes as South Korean authorities examine cybersecurity problems across the financial sector. Bithumb has not disclosed the method used to access its internal system or the full extent of the data exposure.
The breach also follows a separate internal control error at Bithumb in February. The exchange mistakenly credited customers with 620,000 Bitcoin instead of 620,000 South Korean won.
The Bitcoin amount was worth more than $40 billion at the time of the incident. Chief Executive Lee Jae-won acknowledged weaknesses in the exchange’s internal controls after the error. The February incident involved an incorrect credit, while the latest case concerns unauthorised access to an internal system. No available information links the two incidents.
Two More South Korean Firms Report Security Breaches
Bithumb is not the only South Korean financial company facing a security investigation. Daishin Securities and Mirae Asset Global Investments have also reported incidents.
Daishin Securities confirmed that an external attack exposed personal and credit information belonging to 38,490 customers. The brokerage has taken emergency measures in response.
Meanwhile, Mirae Asset detected unauthorised access to some of its web systems and blocked it. The company said investor information was not affected.
South Korea’s Financial Supervisory Service is examining the incidents involving all three companies. It has also sent an inspection team to Daishin Securities.
FSS Governor Lee Chan-jin discussed the recent attacks with bank holding company chairs on October 28. Earlier in October, he said cyber attacks had affected 16 South Korean financial firms by October 14.
