
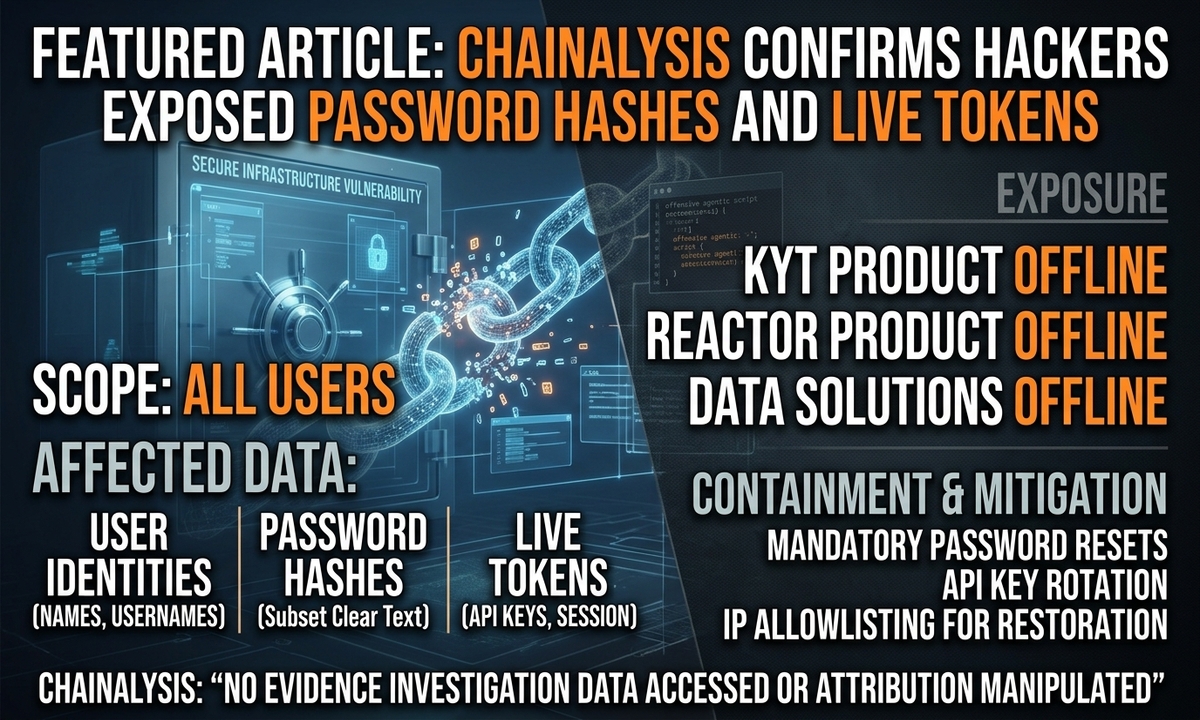
Blockchain analytics firm Chainalysis has confirmed that hackers accessed customer password hashes and live tokens. The attack also exposed names, usernames and other customer details.
In a November 4, 2026 security update, the company revealed new details about the breach. Its initial October 30 report only mentioned exposed user IDs, email addresses, full names and organisational roles.
However, further investigations uncovered an attack that exposed some customer passwords. Chainalysis described the incident as an ongoing, multi-front cyber attack.
The company said hackers used an on-path attack to intercept customer passwords. This method allows attackers to access information exchanged between two parties.
The breach also exposed password hashes and live authentication tokens. Password hashes represent protected versions of stored passwords. Meanwhile, live tokens can allow access to accounts without requiring passwords.
Chainalysis has not disclosed its password hashing method or identified the exposed token types. It also has not confirmed whether attackers used the exposed information to access customer accounts.
The company said it contained the attack method and locked affected accounts. It found no evidence that hackers accessed investigation content, transaction results or customer queries.
Chainalysis also reported no signs of changes to its blockchain attribution data. Meanwhile, external cybersecurity experts are helping investigate the incident.
Security Breach Forces Chainalysis to Suspend Several Services
The attack forced Chainalysis to suspend several services used by cryptocurrency businesses and law enforcement agencies.
On November 2, the company took Reactor and Data Solutions offline for additional security checks. However, the disruption expanded two days later.
Meanwhile, Chainalysis detected suspicious activity involving its Know Your Transaction (KYT) service on November 4. The company responded by suspending the KYT interface and application programming interface (API).
It also restricted access to other address-screening products and its login page. The suspensions affected services that customers use to monitor cryptocurrency transactions and investigate suspicious activity.
The company has recommended that users should reset their passwords and rotate API keys where necessary. However, it has not announced when Reactor and Data Solutions will return.
What Happens Next for Affected Customers?
Chainalysis is still investigating suspicious activity on its KYT service. The company is also contacting customers whose accounts may have experienced unauthorised access.
Meanwhile, it has warned customers against clicking links in unexpected password reset emails. It also advises users to change any passwords they reused on other platforms.
In addition, Chainalysis has recommended that organisations enable two-factor authentication. It has also urged customers to report suspicious messages and account activity to their security teams.
The incident comes amid several security breaches in the cryptocurrency industry. Binance suffered an estimated $6.3 billion crypto hack on October 29. However, Chainalysis said its incident had no connection to the Binance attack. Chainalysis also helped coordinate the freezing of nearly $10 million in stolen cryptocurrency following the Mercado Bitcoin attack.
