
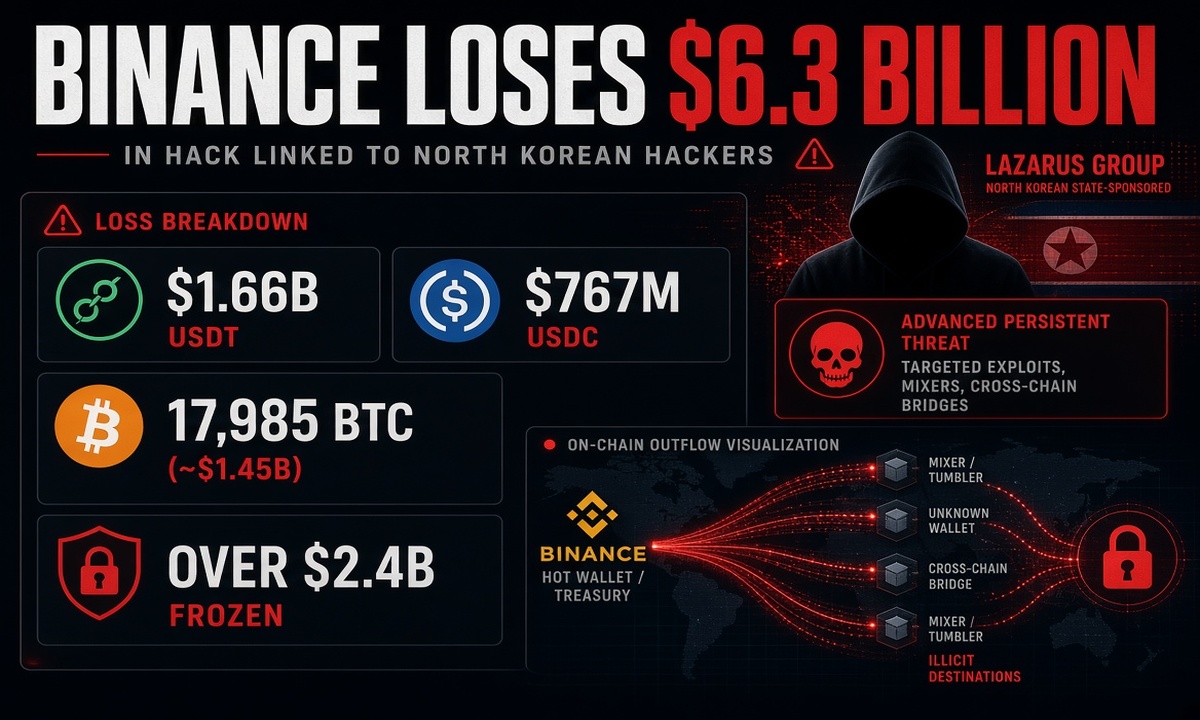
Binance is facing a major security breach after attackers stole approximately $6.36 billion from its cryptocurrency wallets on Thursday, October 29, 2026.
Blockchain intelligence firm TRM Labs linked the attack to TraderTraitor, a North Korean hacking unit associated with Lazarus Group.
TRM Labs attributed the attack to TraderTraitor with high confidence. However, Binance has not confirmed the attackers’ identity. Blockchain investigator ZachXBT also identified Lazarus as the likely culprit.
The attackers targeted wallets across ten blockchain networks, with Ethereum accounting for approximately $3.79 billion. Bitcoin followed with $1.47 billion, while Tron accounted for another $628 million.
The hackers also withdrew 233.46 million XRP, worth nearly $296 million, from five Binance wallets. These transfers happened before the main Ethereum attack.
TRM Labs traced the main wave of transactions to approximately 20:05 UTC on October 29. The attackers moved most of the stolen funds within 20 minutes.
Investigators also found evidence of preparations before the breach. An attacker-controlled wallet received three small Tornado Cash withdrawals at least 36 hours before the theft. The attackers then tested malicious code before targeting Binance.
The suspected hacking unit has faced similar accusations before. The FBI linked TraderTraitor to the February 2025 Bybit hack, which cost the exchange approximately $1.5 billion.
Binance Wallet Exploit Raises Questions About Internal Security
Blockchain security firm Blockaid identified 50 EIP-7702 authorisations targeting Binance 14, an Ethereum hot wallet.
EIP-7702 allows Ethereum wallets to authorise smart contract code to execute actions on their behalf. The attackers exploited this feature to gain control over the targeted wallet.
They prepared 50 authorisations using consecutive transaction counters to increase their chances of success. Only one authorisation worked, allowing a malicious contract to transfer assets.
The exploit enabled the attackers to drain approximately $2.5 billion from Binance 14. The stolen funds included 167,464 ETH and more than 1.6 billion USDT. The malicious contract could also transfer new deposits entering the wallet.
Meanwhile, Binance’s initial investigation pointed to a possible compromise involving a DevOps engineer’s laptop. The exchange said the device may have provided unauthorised access to an internal service container.
TRM Labs suspects that attackers also accessed Binance’s transaction-signing infrastructure. However, Binance reported no evidence of leaked private keys during its initial investigation. The exchange plans to publish a detailed report after establishing how the attackers accessed its systems.
Chanpeng Zhao’s Exchange Freezes Assets as Withdrawals Remain Suspended
Binance pledged to cover customer losses through its Secure Asset Fund for Users (SAFU) and company resources. Several companies and security teams have also restricted access to funds linked to the attack. Tether froze more than $1.567 billion in USDT, while Circle reported freezing over $800 million in USDC.
In addition, the Arbitrum Security Council secured approximately 74.6 million ARB and 8,425 ETH associated with the attacker. Binance reported approximately $3 billion in frozen assets.
However, the attacker still controlled nearly 480,720 ETH worth approximately $1.08 billion, according to Onchain Lens. The tracker also identified a separate transfer of 17,260 ETH worth $38.82 million to another wallet.
Binance suspended withdrawals while upgrading its security systems and strengthening address controls. Deposits remain operational, and the exchange expects withdrawals to resume within 48 hours.
Bitcoin briefly fell below $77,000 following the breach, while derivatives liquidations exceeded $1.5 billion over 24 hours.
